-
Internal VLAN interconnection of 1 core switch
# Create interconnection VLANs on the core switch and add interfaces to the interconnection VLANs. Configure interfaces for. Virtual Local Area Network (VLAN) helps break a large network into smaller, manageable parts, improving security and efficiency. However, VLANs are isolated from one another by default, meaning devices in different VLANs cannot communicate unless we enable Inter-VLAN Routing. When a frame needs to cross between switches, it gets a 4-byte tag saying "I belong to VLAN 20. VLAN might not be enabled on the trunk ports.
-
US Core Switch Configuration
Below is the list of US Core Profiles. Each profile identifies which core elements, extensions, vocabularies, and ValueSets SHALL be present in the resource when using this profile. Together, they promote i.
-
Is the core layer switch managed
The roles of distribution and core switches demand the granular, Layer 3 control that only managed switches provide. Their functions in routing, security, and high-availability are non-negotiable. Engineered to aggregate massive volumes of data from distribution switches, it provides ultra-low latency and maximum throughput to ensure uninterrupted routing and packet. Core Layer: The core layer is the backbone of the hierarchy network. Access switches should be smart or fully. Our company has 200-250 devices connected to the network which includes laptops, mobile phones, CCTVs, IP Phones,Access Points, Network Printer, Biometrics, Door Locks, Kramer VIA (Wireless Platform),2 NAS for HA, 2 Rack Server for HA w/ Virtual Machines (Active Directory, Zabbix & Grafana, Point. A core switch is the backbone of a large-scale network, designed to handle massive volumes of traffic with ultra-low latency and maximum reliability. It can be considered a central network layer that performs all the functions, like monitoring traffic and empowering the whole system. In actuality, there are three primary layers of a complex network.
[PDF Version]
-
Which layer is the core network switch on
A core switch is a high-capacity, high-performance Layer 3 switch positioned at the physical backbone of an enterprise network. The primary transmission and routing of data signals take place at the core layer only. It can be considered a central network layer that performs all the functions, like monitoring traffic and empowering the whole system. Simply put, it's the kingpin that keeps your network humming.
-
How to configure a Layer 3 core switch for a router
To start using layer 3 routing, navigate to the Switching > Configure > Routing & DHCP page. You can configure a port as a Layer 2 interface or a Layer 3 interface. A routed interface is a physical port that. Layer 3 switches provide the routing function, which indicates a network-layer function in the OSI model. This example uses router configurations of AR3600 V200R007C00SPCc00. The latest Cisco Catalyst Switches are equipped with the Enhanced Multilayer Image (EMI), which can work as a Layer 3 device with full routing capabilities, also known as a multi-layer switch (MLS). Currently, at each location, we have our ISP router connected to a little unmanaged switch, which then is. A routed port is a physical port on a switch or router that is configured to act as a Layer 3 interface. Unlike regular switch ports, a routed port is not associated with a specific VLAN and does not participate in Layer 2.
[PDF Version]
-
Israeli Core Switch NRZ
NRZ can refer to any of the following line codes: The NRZ code also can be classified as a polar or. In telecommunications, a non-return-to-zero (NRZ) line code is a binary code in which ones are represented by one significant condition, usually a positive voltage, while zeros are represented by some other significant condition, usually a negative voltage, with no other neutral or rest condition. For a given data signaling rate, i.e., bit rate, the NRZ code requires only half the baseband band. Comparison with return-to-zero describes a used in in which the signal drops (returns) to zero between each. This takes place even if a number of consecutive 0s or 1s occur in the signal. The signal is. • Brey, Barry (2006). The Intel Microprocessors. Columbus:.• Savard, John J. G. (2018). quadibloc. from the original.
-
Substation Network Management Industrial-Grade Switch
Designed for substation automation, this portfolio focuses on power-utility EMC immunity, wide temperature durability, fast network recovery, and precise time synchronization —with flexible rackmount or DIN-rail installation and AC/DC redundant power. To meet the growing demand for digital substations, Westermo offers industrial Ethernet switches compliant with IEC 61850-3. Substations and power utilities are mission critical systems where 100% reliability is a must and Westermo switches are designed with these requirements in the forefront. They connect protection relays, merging units, bay controllers, SCADA gateways, time servers, HMIs, and many more devices. If a switch fails or behaves incorrectly, the entire communication system can be affected.
-
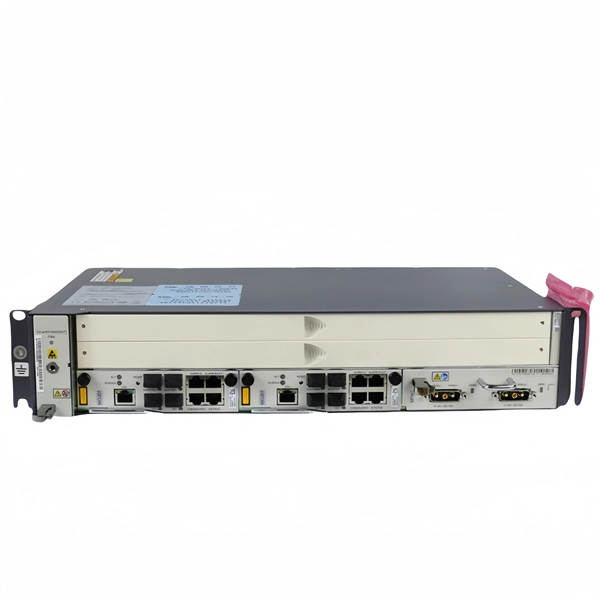
How to debug IP on an access switch
You can not do a debug ip packet on a named ACL. Add log keyword on your ACL permit and deny rules. By adding "log" to these rules, any traffic that matches them will be logged in your device's syslog. The question is which commands expose that evidence and how to read the output without chasing red. With Cisco debug command, we display information about Cisco router & switch operations, activities or errors in real time. Cisco Packet Tracer Cisco Configurations Course! During the troubleshooting, we turn on debug and get. This appendix describes the debug privileged EXEC commands that have been created or changed for use with the Catalyst 2960 switch. These commands are helpful in diagnosing and resolving internetworking problems and should be enabled only under the guidance of Cisco technical support staff. Because. This is a comprehensive list of essential ACI troubleshooting commands for controllers, leaves, and spines. In the below example, we enable IP packet debugging on R2.
[PDF Version]
-
H3 Switch C Check Optical Port Optical Attenuation
Run the following command to view the Digital Diagnostic Monitoring (DDM) data of the optical module: show transceiver diagnosis interface <interface-type> <interface-number> The output provides real-time diagnostic metrics and their corresponding threshold ranges. The following uses the Moduletek QSFP-40G-LR4 module connected to an H3C S6820 switch as an example to introduce how to read information of the connected optical module on an H3C switch. Figure 1 Schematic Diagram of Optical Module Connected to Switch 1. If the same port with the same optical module has link, then I do get a proper readout of the optical monitor command (tx power / rx power / temps / current). Being able to monitor a non-working link is a pretty basic thing to do to be honest and having access to DDM/DOM/optical monitoring of down. l This document discusses the commands specific to Ethernet Passive Optical Network (EPON).
[PDF Version]